Download this white paper to examine the architectural and security considerations associated with specialized networks and learn how data center operators can protect critical data and communications without compromising the performance demanded by distributed AI and HPC workloads.
Search Results for: security
Rambus Enhances Enterprise-Grade Security for Data Center and AI SoCs with CryptoManager™ Root of Trust Supporting the Caliptra™ Specification
CryptoManager Root of Trust for use with Caliptra specification provides a production-ready Root of Trust and security orchestration solution that accelerates deployments and enables advanced security for mission-critical data center and AI infrastructure devices
- Provides Root of Trust and security orchestration interoperable with the open-source Caliptra framework
- Accelerates customer deployments with a complete hardware and software integration framework, including dedicated drivers, APIs, and system-level security applications
- Delivers best-in-class side-channel protection, cryptographic agility, integration flexibility, and support for data center and AI SoC designs
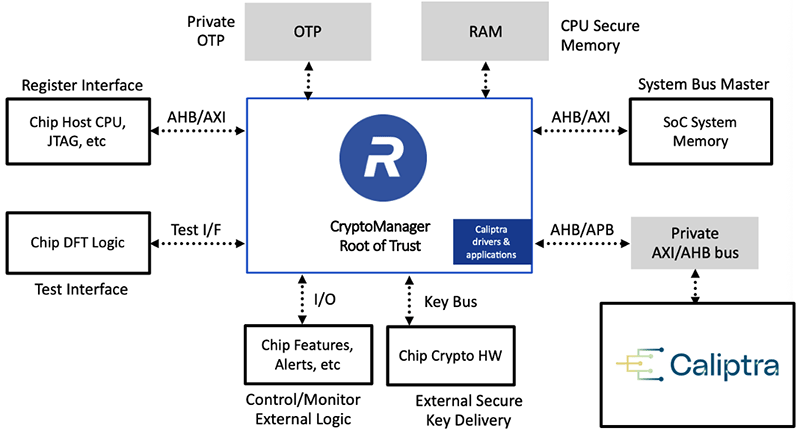
Figure 1: CryptoManager Root of Trust Supporting Caliptra Specification
SAN JOSE, Calif. – Sep. 14, 2026 – Rambus Inc. (NASDAQ: RMBS), a premier chip and silicon IP provider making data faster and safer, today announced its CryptoManager™ Root of Trust supporting the Caliptra™ specification, a production-ready Root of Trust and security orchestration solution designed to deliver enterprise-grade security for mission-critical data center and AI SoCs. Interoperable with the open Caliptra framework, the Rambus solution helps semiconductor designers accelerate deployments with added protection, flexibility and support. CryptoManager Root of Trust delivers platform-wide security awareness with proven side-channel and fault-injection protections and best-in-class cryptographic agility for a low-risk path to volume implementations of highly secure data center and AI infrastructure devices.
Caliptra is an open-source silicon Root of Trust designed for integration into data center-class SoCs. Initiated through the Open Compute Project and now developed within the CHIPS Alliance, it combines hardware, firmware and specifications to provide a common foundation for device identity, measured boot and attestation across CPUs, GPUs, AI accelerators, DPUs, networking devices and other infrastructure components. Its transparent, collaborative model supports greater consistency across devices from different suppliers.
Production-Ready Security for Customer Caliptra Deployments
With the CryptoManager Root of Trust supporting the Caliptra specification, designers can build on the open-source foundation to implement a complete production security subsystem. This addresses integration into the wider platform, provides the software and security orchestration needed for deployment, adds protection against advanced attacks, supports evolving cryptographic requirements, enables additional security certifications and maintains the solution throughout the device lifecycle.
“As the Caliptra ecosystem gains momentum, organizations need a practical path to deploy scalable and supportable security solutions in demanding production environments,” said Simon Blake-Wilson, SVP and general manager of Silicon IP at Rambus. “CryptoManager Root of Trust supporting the Caliptra specification provides the hardware, software, advanced protections and commercial support needed to accelerate deployment of differentiated, enterprise-grade security that is interoperable with the Caliptra framework.”
The CryptoManager Root of Trust supporting the Caliptra specification provides dedicated hardware-level security in an SoC, combining a secure RISC-V processor, protected memory, secure key and data storage, cryptographic accelerators, and secure interfaces. Operating alongside an unmodified open-source Caliptra Project core, it mediates interactions between the Caliptra Project core, the host processor and other SoC components so that security-sensitive operations can remain within a protected boundary while trust is extended across the wider platform.
Through specialized drivers and security applications, CryptoManager Root of Trust provides platform-level awareness enabling security monitoring, policy enforcement, secure lifecycle management, and coordinated protection of critical system resources. The CryptoManager architecture supports classical, post-quantum, and regional cryptographic algorithms, along with advanced protections against side-channel and fault injection attacks, and certification support for security standards such as FIPS 140-3 and SESIP.
By combining enterprise-grade security with simplified integration and certification readiness, the CryptoManager Root of Trust delivers a production-ready security platform for next-generation data center and AI semiconductor devices.
More Information
Learn more about the Rambus CryptoManager Root of Trust supporting the Caliptra specification here.
Forward-Looking Statements
Information set forth in this press release, including statements as to Rambus’ outlook and financial estimates and statements as to the expected timing and effects of Rambus products, constitute forward-looking statements within the meaning of the safe harbor provisions of the Private Securities Litigation Reform Act of 1995.
These statements are based on various assumptions and the current expectations of the management of Rambus and may not be accurate because of risks and uncertainties surrounding these assumptions and expectations. Factors listed below, as well as other factors, may cause actual results to differ significantly from these forward-looking statements. There is no guarantee that any of the events anticipated by these forward-looking statements will occur, or what effect they will have on the operations or financial condition of Rambus. Forward-looking statements included herein are made as of the date hereof, and Rambus undertakes no obligation to publicly update or revise any forward-looking statement unless required to do so by federal securities laws.
Major risks, uncertainties and assumptions include, but are not limited to: any statements regarding anticipated operational and financial results; any statements of expectation or belief; other factors described under “Risk Factors” in Rambus’ Annual Report on Form 10-K and Quarterly Reports on Form 10-Q; and any statements of assumptions underlying any of the foregoing. It is not possible to predict or identify all such factors. Consequently, while the list of factors presented here is considered representative, no such list should be considered to be a complete statement of all potential risks and uncertainties.
Caliptra™ is a trademark of The Linux Foundation and is managed under the CHIPS Alliance project. All rights reserved. Any use of the Caliptra name or logo in this document is purely for descriptive, educational, or reference purposes and does not imply endorsement, sponsorship, or affiliation with The Linux Foundation or CHIPS Alliance.
Beyond Trusted: What the NSA’s New Guidance Means for Hardware Security
On August 25, 2026, the National Security Agency (NSA), working with the Joint Federated Assurance Center Hardware Assurance (JFAC HWA) laboratories, released two technical reports addressing intentional threats to application-specific integrated circuits during design and manufacturing: the “ASIC Best Practices Threat Catalog” and “Application Specific Integrated Circuit Level of Assurance 1 (LoA1) Best Practices”. The LoA1 report is the first of three planned reports intended to establish Levels of Assurance for custom microelectronic hardware. [1,2]
The release is commendable and significant not because it replaces the Department of War (DoW) existing Trusted microelectronics requirements but because it provides a detailed framework for addressing what happens when Trust cannot encompass the entire semiconductor lifecycle.
That distinction matters as DoW increasingly relies on a commercial semiconductor ecosystem spanning third-party intellectual property, electronic design automation tools, commercial foundries, packaging providers, suppliers, and globally distributed technology.
NSA’s guidance is important because it recognizes that reality while remaining squarely within existing DoD policy. It begins with the requirement to use accredited Trusted processes where they apply, then explains how programs should evaluate and mitigate lifecycle risks when those processes do not cover every activity, supplier, or technology needed for a given ASIC.
Trust and Assurance Are Not the Same Thing
The new guidance begins firmly within existing policy. It points programs to DOD Instruction (DoDI) 5200.44 and states that DoW programs must use processes and suppliers accredited through the Defense Microelectronics Activity trusted process unless a waiver is requested.
But the guidance also addresses an important practical reality: trusted processes or services may not always be available.
When that occurs, or when a program determines that additional validation is necessary, JFAC recommends additional mitigations. The report goes further: unless the entire ASIC development and manufacturing effort is conducted by accredited trusted suppliers, programs should use additional validation to identify and mitigate risk associated with lifecycle activities conducted outside the trusted process. [2]
The Trusted model establishes accredited processes and services across activities such as design, aggregation, fabrication, packaging and assembly, and test. It is supported by requirements governing the people, facilities, systems, and suppliers involved. Assurance addresses the broader question of how confidence in the resulting device is established against mission-relevant threats.
Where the trusted boundary ends, assurance does not end with it.
For DoW, that creates a path to use technologies and capabilities that cannot all practically reside inside one large, trusted ecosystem while still addressing risks created outside that boundary.
The Threat Surface Is the Semiconductor Lifecycle
One of the most useful aspects of the new guidance is the breadth of the threat model.
The report considers potential adversary compromise beginning with design requirements and extending through IT systems, EDA software, third-party IP, HDL, design scripts, netlists, foundry process-design information, physical design, tapeout, wafer manufacturing, test, personalization, dicing, packaging, delivery, and user documentation. [2]
That framing is important because even when trusted processes are used across design, fabrication, packaging, and other portions of the lifecycle, assurance still depends on understanding where threats can be introduced and whether the controls applied at each stage are sufficient for the mission.
A compromised third-party IP block presents a different threat from manipulation of an EDA environment, unauthorized modification of a design artifact, malicious changes during fabrication, or compromise during packaging and test. Each occurs at a different point in the lifecycle and may require different methods of prevention, detection, verification, or mitigation.
Assurance therefore cannot be reduced to the trustworthiness of a single supplier, facility, or process. It must consider the chain of technologies, processes, organizations, and people involved in turning requirements into a delivered device, and the threats and consequences relevant to each.
Start With the Threat, Not the Mitigation
Perhaps the most important idea in the guidance is also one of the simplest: programs must understand their own threat environment.
The report’s threat catalog provides a starting point, but NSA/JFAC places responsibility on government program offices and their performers to evaluate and understand their threat space and define appropriate protection. The guidance then provides multiple mitigation options so programs can tailor an approach to their needs. [2]
That is an important architectural principle.
Hardware assurance should not begin with a predetermined security technology and work backward to justify its use. It should begin with the mission. What functions are critical? What happens if the device is subverted? What adversary capabilities are relevant? Where can an adversary gain access? What would an effective attack require?
From there, programs can determine the assurance required and select technical and procedural mitigations appropriate to the risk.
The LoA construct makes that approach more systematic. For LoA1, the framework characterizes threats according to five factors: access, technology, investment, value of effect, and targetability. LoA1 applies to ASIC-based designs where system failure could meaningfully reduce a U.S. Government capability while essential operational capabilities would remain available. [1,2]
This is not an argument for less assurance. It is an argument for assurance commensurate with mission and threat.
The Security Boundary Includes More Than Technology
Another important aspect of the guidance is the attention it gives to the environment in which an ASIC is developed.
The report addresses assurance planning, acquisition considerations, third-party IP, EDA software, protected design-flow environments, role-based access controls, verification and test planning, design repositories, and acceptance criteria for design artifacts. [2]
That matters because a security boundary is not merely a physical boundary around a semiconductor facility or a server. It can include people: who has access to design information, who can modify an artifact, what privileges they possess, how changes are reviewed, how third-party IP enters the design, how tools are controlled, and how design integrity is maintained as it moves toward production.
The semiconductor itself is the end product of a much larger technical and human system.
Reducing the size of the boundary therefore does not mean ignoring those dependencies. It means understanding which dependencies exist and where verification, validation, monitoring, technical controls, and other assurance mechanisms can establish the necessary confidence and resilience.
The Commercial Semiconductor Ecosystem Makes This Increasingly Important
DoW does not operate independently of the commercial semiconductor industry. State-of-the-art microelectronics increasingly depend on commercial technologies, tools, IP, manufacturing capabilities, and suppliers distributed across a complex ecosystem.
The new NSA/JFAC guidance provides a practical framework for addressing that problem at the ASIC level: it identifies relevant threats and offers mitigation options across the development and manufacturing lifecycle.
That is particularly important for DoW because it allows the assurance discussion to begin with mission risk rather than with an assumption that every device, application, or lifecycle stage requires the same controls. Different missions, devices, threats, and consequences of compromise can require different protections.
And Then Comes Heterogeneous Integration
The guidance primarily addresses single-die packaged ASICs. It states that multi-chip modules, 3D packaging, and other ASIC configurations are outside its primary scope, although portions of the guidance may still apply. Firmware and software running on the ASIC are also outside its scope, and confidentiality is generally treated as a security concern rather than an assurance concern except where the two intersect. [2]
That scope provides an important foundation for ASIC assurance, and it could point toward the next challenge.
DoW systems are increasingly moving toward heterogeneous integration and chiplet architectures, where independently designed and manufactured components can be combined within a common package or system. Those components may come from different suppliers and foundries, use different process technologies, perform different functions, and carry different assurance characteristics.
Assuring each component remains essential. But component assurance alone cannot tell us whether the resulting system is secure.
When components are brought together, new boundaries are created. Components must identify and communicate with one another. Information and security state cross interfaces. One component may be allowed to access resources belonging to another. A security-critical component may sit beside a commercial accelerator developed for an entirely different threat environment.
Putting those components inside the same package does not make them secure. And it should not automatically make the package itself the security boundary.
That means the next question for hardware assurance is not simply how to apply today’s ASIC mitigations to every chiplet. It is how component-level assurance, security boundaries, security architecture, interfaces, and system behavior come together to establish confidence in a heterogeneous system.
NSA and JFAC’s new ASIC guidance provide an important foundation for answering that question.
It will be exciting to see the next steps and how the community builds on it.
This is the first in a series examining the evolution of hardware assurance as Defense moves toward assurance of increasingly heterogeneous microelectronics. The next article will examine how RAMP, RAMP-C, and SHIP helped establish the commercial and assurance foundations for heterogeneous Defense microelectronics—and why chiplet architectures can make security architecture a system-level solution from the beginning.
References
[1] National Security Agency. NSA Releases Best Practices to Mitigate Threats in Development of ASICs. August 25, 2026.
[2] National Security Agency, Cybersecurity Directorate, and Joint Federated Assurance Center Hardware Assurance Laboratories. DoW Microelectronics: Application Specific Integrated Circuit Level of Assurance 1 Best Practices. Version 1.0, August 2026. U/OO/6055347-26, PP-26-3181.
Reliability and Supply Chain Security for the Automotive Semiconductor Industry
[Live on May 21 at 11am PT] This webinar examines why reliability and security have become inseparable drivers for next‑generation automotive chips, and how a lifecycle‑based approach is required to meaningfully reduce recall risk. We will review real‑world examples of recalls caused by electronic failures, explore the evolving standards landscape driving higher expectations for reliability and traceability, and walk through the end‑to‑end chip lifecycle from wafer fabrication to in‑vehicle operation.
Rambus Announces Industry-Leading Ultra Ethernet Security IP Solutions for AI and HPC
AI/HPC clusters process a tremendous volume of valuable data and have already become a critical element of modern infrastructure and therefore must be protected at all levels that are exposed to potential threats. Network security is one of the key components aiming to provide:
- Access control – allowing only the authorized nodes or users to access the compute systems
- Data confidentiality – encrypting data on the wire and protecting the encryption keys from being recovered
- Data isolation – using different secure domains and encryption keys for data belonging to different applications, jobs, or users
- Threat detection – ability to identify manipulations with the data and critical network headers, identify packets being replayed, delayed, etc.
Because of the scale and cost of each AI/HPC system, there is a need to support a high level of utilization for return on investment. This requires the network security feature to keep up with the overall AI/HPC system goals:
- High throughput, ideally full line rate
- Minimal impact on latency
- Efficiently support the system scale (number of ports, nodes, secure domains)
- Have reasonable cost of silicon area and power
Ultra Ethernet Tailored for AI and HPC
The Ultra Ethernet Consortium (Ultra Ethernet Consortium) was set up in 2023 by leading companies in HPC and connectivity with the goal of enhancing Ethernet’s capabilities through standardizing a high-performance Ethernet stack purpose-built for the unique demands of AI/HPC.
UEC specification v1.0 that was publicly released in June 2025 defines a transport protocol (UET) that provides the ability to deliver data straight from the network and into application memory and vice versa, without software involvement. This method is known as “Remote DMA”. The new transport protocol brings numerous enhancements to the current, widely used RoCE v2 (RDMA over converged network) and both are going to co-exist for some time. For transport protocol protection, UEC defined a Transport Security Sub-layer (TSS), which leverages concepts from IPsec and PSP (Google’s open-source security protocol) to efficiently support multiple use cases at scale. The TSS is a new protocol, therefore it is not compatible with any of the previously defined protocols while the implementation is going to have a lot in common with line-rate MACsec and IPsec solutions.
TSS protocol is defined in such a way that it is applied to protect the payload and optionally authenticate network headers, leaving the routing and load balancing information accessible. TSS also allows leaving parts of the UEC transport headers in clear for ease of inspection and debugging. This means that fabric switches do not need to deal with the TSS layer, and its presence in the packet is transparent for the network operation. Therefore, TSS is going to be added only to SmartNICs, and the market is going to have two flavors of SmartNICs: UEC-only (requiring only TSS for security) and UEC+RoCE (requiring TSS along with IPsec and if required, MACsec).
Rambus Security IP for Ultra Ethernet TSS
Rambus, having successfully served the data center, enterprise and infrastructure markets with line rate MACsec and IPsec products (Secure Networking), adds two new solutions for securing UET transport protocol with TSS:
- UET-TSS-IP-69, an inline, multi-channel TSS transformation engine at rates up to 1.6Tbps for customers who already have the classification and policy databases in place.
- UET-TSS-IP-369, an inline, high-performance, multi-channel packet engine that provides a complete TSS layer at rates up to 1.6Tbps. It embeds the UET-TSS-IP-69 as processing data path and complements it with classification, SDKDB, key management and statistics.

UET-TSS-IP-369 Block Diagram
Both of these UET-TSS IP solutions are expected to be used in SmartNICs and NIC chiplets, and in the future to be part of UET-based NVMe-oF storage controllers. As IP blocks that can be instantiated independent of the ethernet controller, the Rambus UET-TSS IP solutions can support customers’ own tunneling protocols while providing flexibility and scalability. With over three decades of state-of-the-art security expertise, Rambus offers the industry’s broadest and most performant portfolio of security IP solutions backed by world-class support from Rambus security experts. For complete details, please visit Rambus Security IP.
Secure by Design Series: UEC Security: Delivering High-Performance, Scalability and Secure Networking for AI and HPC
[Live on March 19] As AI and HPC workloads accelerate, next-generation data center fabrics must deliver unprecedented throughput without compromising security. The Ultra Ethernet Consortium (UEC) is redefining high-performance networking with a new transport architecture designed for RDMAclass efficiency and massive scale. In this webinar, we will demystify UEC’s security model, purpose-built to protect scale-out networks running over dedicated AI/HPC fabrics.