At Rambus, we create cutting-edge semiconductor and IP products, providing industry-leading chips and silicon IP to make data faster and safer.
CryptoManager Root of Trust for Use with the Caliptra Specification
Root of Trust and Security Orchestration for Caliptra-based SoCs
Home > Security IP > Root of Trust Solutions > CryptoManager Root of Trust for Use with the Caliptra Specification
The Rambus CryptoManager Root of Trust for use with the Caliptra specification is a production-ready Root of Trust and security orchestration solution that complements the open Caliptra framework to deliver enterprise-grade silicon security. As adoption of Caliptra expands across data center, AI, networking and infrastructure devices, designers need more than a foundational Root of Trust. CryptoManager Root of Trust for use with the Caliptra specification adds protection, flexibility, support and certification readiness required for commercial silicon deployments.
For vendors seeking Caliptra trademark compliance, CryptoManager Root of Trust for use with the Caliptra specification provides the capabilities needed to transform an open-source security foundation into a deployable solution. While Caliptra establishes a common Root of Trust architecture, CryptoManager Root of Trust adds platform-wide security awareness, proven side-channel and fault injection protections, cryptographic agility, certification readiness, simplified integration, expanded functionality and direct Rambus support. The result is a low-risk path to deployment that preserves Caliptra compatibility while delivering enterprise-grade security.
 Contact
 Product Brief
 Security Certifications
From Caliptra Foundation to Full Deployment
As AI infrastructure and modern data centers become increasingly dependent on heterogeneous processors, accelerators, and controllers, establishing trust in every device has become a critical security requirement. This white paper examines how the open-source Caliptra Root of Trust framework provides a common foundation for device identity, measured boot, and attestation across data center-class systems, while highlighting the challenges and means of transforming an open standard into a production-ready deployment. By enabling organizations to preserve alignment with the Caliptra ecosystem while accelerating deployment and reducing integration risk, a practical path from open-source Root of Trust adoption to enterprise-grade security implementation for data center and AI infrastructure can be realized.
How the CryptoManager Root of Trust for Use with the Caliptra Specification Works
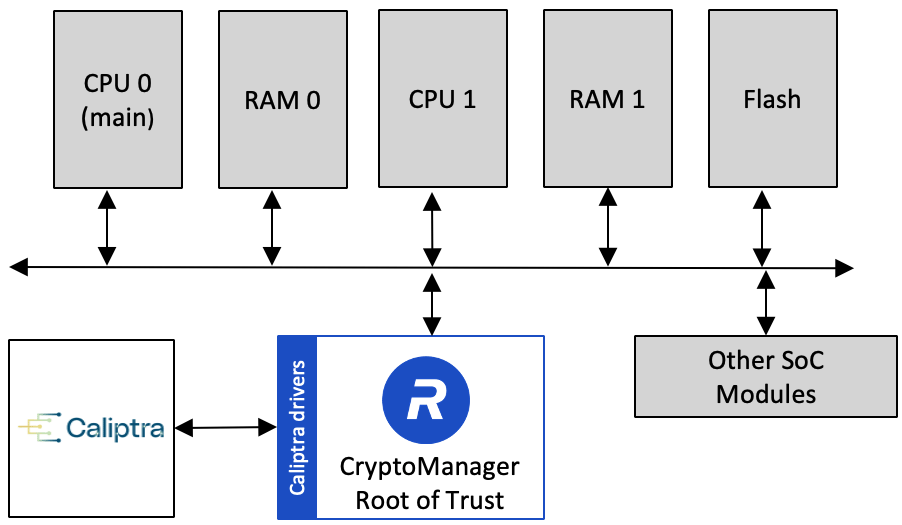
CryptoManager Root of Trust for use with the Caliptra specification is integrated as a dedicated hardware security subsystem within the SoC, combining a secure RISC-V processor, protected memory, secure key and data storage, cryptographic accelerators, and secure interfaces. Operating alongside the Caliptra core, it provides a trusted foundation for device security while maintaining compatibility with the Caliptra ecosystem.
Through specialized Caliptra drivers and security applications, the CryptoManager Root of Trust extends security visibility beyond the Root of Trust itself to the broader SoC. This platform-level awareness enables security monitoring, policy enforcement, secure lifecycle management, and coordinated protection of critical system resources.
CryptoManager Root of Trust for use with the Caliptra specification performs security-critical functions including secure boot, firmware authentication and updates, device identity management, attestation, key provisioning, secure communications, and cryptographic services. Sensitive assets remain protected within the trusted boundary, while hardware-enforced isolation prevents unauthorized access to keys, credentials, and security operations.
The architecture supports classical, post-quantum, and regional cryptographic algorithms, along with advanced protections against side-channel and fault injection attacks. By combining enterprise-grade security, simplified integration and certification readiness, CryptoManager Root of Trust for use with the Caliptra specification delivers a production-ready security platform for next-gen semiconductor devices.
Solution Offerings
- Production-ready Root of Trust solution for Caliptra-based SoCs
- Designed to support Caliptra trademark-compliant implementations using unmodified Caliptra core RTL and firmware
- Secure RISC-V processor with protected memory and secure execution environment
- Platform-wide security orchestration with visibility beyond the Root of Trust boundary
- Secure boot, secure firmware update, attestation and device identity services
- Hardware-protected key and data storage with secure provisioning support
- Classical cryptography including AES, SHA, RSA and ECC algorithms
- Post-quantum cryptography support including ML-KEM, ML-DSA, SLH-DSA and LMS algorithms
- Regional cryptography support including Chinese SM2, SM3 and SM4 algorithms
- Advanced side-channel attack and fault injection attack countermeasures
- Secure communications and lifecycle security management capabilities
- FIPS 140-3, PSA and SESIP certification support and deployment readiness
- Comprehensive hardware, software and integration documentation & support
- Complete source package and SDK
- Pre-built Caliptra drivers
- Supervisor-level security applications
- Hardware integration guide
- System-level integration guide
- FPGA reference design package
Tools and Scripts
- Verilog for synthesis and simulation
- All scripts and support files needed for standard EDA tool flows
Integration Deliverables
- Complete verification test bench and comprehensive set of test vectors
- Boot loader and firmware, including secure RTOS and security monitor
- HLOS APIs for accessing capabilities
- Complete development environment, including compiler, assembler, debugger, simulator, reference code