Contact
 Product Brief
 Security Certifications
At Rambus, we create cutting-edge semiconductor and IP products, providing industry-leading chips and silicon IP to make data faster and safer.
By Bart Stevens, Senior Director of Product Marketing at Rambus
The cybersecurity threat landscape is dynamic and rapidly evolving. Indeed, attackers are constantly finding new ways to exploit critical vulnerabilities across a wide range of applications and devices. Protecting data and devices requires secure processes running on systems and networks.
A Root of Trust is the foundation on which all secure operations of a computing system depend. It contains the keys used for cryptographic functions and enables a system-wide secure boot process. It is inherently trusted and therefore must be secure by design. The most secure implementation of a root of trust is in hardware safeguarding it from malware and non-invasive or invasive tamper attacks. As such, it can be a stand-alone security module or implemented as a security module within a processor or system on chip (SoC).
Chip makers have varying levels of security expertise and desire for integration. For some customers, a fully turnkey hardware Root of Trust would be ideal. Others wish to build their own Root of Trust but would still like to take advantage of the latest state-of-the-art cryptographic accelerators.
To address these varying customer needs, Rambus has introduced a new three-tier architecture in its industry-leading, 3rd generation CryptoManager Root of Trust security IP solutions, namely the CryptoManager Root of Trust, Hub and Core families. The CryptoManager Security IP offerings deliver progressively higher levels of functional integration and security, enabling customers to choose the level of security features and capabilities best suited to their unique requirements.
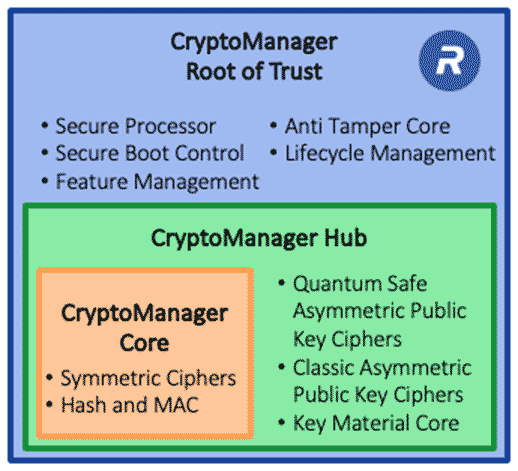
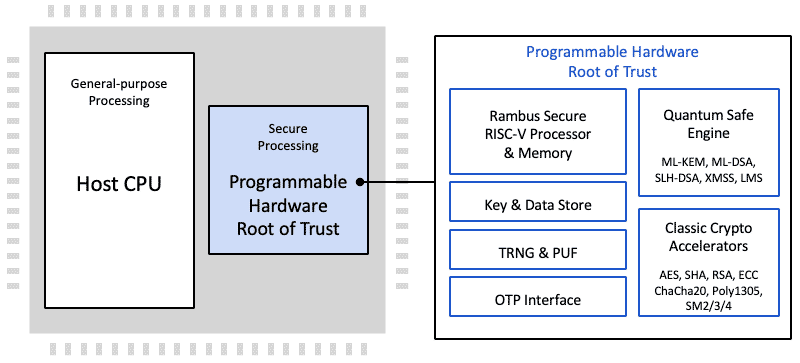
At the highest tier of the architecture is the programmable CryptoManager Root of Trust. The CryptoManager RT-6xx v3 Root of Trust is the latest generation of fully programmable FIPS 140-3 compliant hardware security cores offering Quantum Safe security by design for data center and other highly secure applications, including OCP compliant Caliptra Root of Trust for Measurement with secure boot flow. The CryptoManager RT-6xx family protects against a wide range of hardware and software attacks through state-of-the-art side channel attack countermeasures and anti-tamper and security techniques. With Quantum Safe Encryption (QSE), it provides a future-proof hardware security solution to protect the boot flow and data assets today and into the quantum era.
The CryptoManager RT-6xx allows customers to develop secure and trusted applications that run securely within a trusted boundary. Secure applications can be assigned unique roots and keys, allowing independent permissions and access levels. The RT-6xx inherits its flexible cryptographic accelerators from the embedded Rambus CryptoManager Hub CH-6xx which we’ll describe in the next paragraphs.
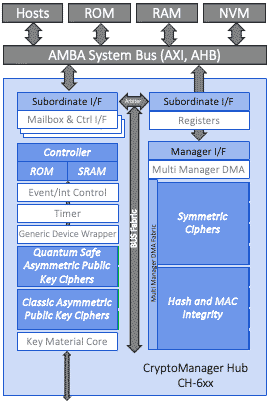
The second tier of the CryptoManager architecture is the CryptoManager Hub CH-6xx, a flexible and configurable, efficient bundle of cryptographic accelerator cores. The CH-6xx family products are intended for embedding in customer or Rambus Root of Trust security modules.
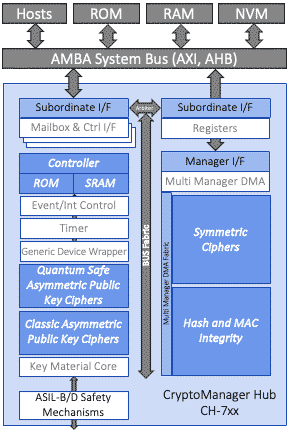
Every CryptoManager Hub embeds a CryptoManager Core (tier 3 of the architecture), a collection of efficient symmetric crypto accelerators with state-of-the-art DMA. The CryptoManager Hub adds firmware-controlled public key infrastructure comprising of a true random number generator, classic and, optionally, Quantum Safe accelerators.
Featuring a controller-based design with dedicated secure memories, the CryptoManager Hub offers a variety of classic asymmetric cryptographic accelerators including RSA, ECC, SM2, TRNG, KDF (Key Derive), KAS (Key Agreement), as well as Quantum Safe accelerators like ML-DSA, ML-KEM and SLH-DSA. CryptoManager Hub is offered in off-the-shelf configurations, allowing a choice tailored to the needs of the customer’s application.
The CryptoManager Core, available as a standalone product leveraging a Host CPU or embedded in the Hub, bundles symmetric crypto accelerators for AES, SM4, ChaCha20, SHA-2, SHA-3, SHAKE, SM3 and Poly1305 behind a multi-channel DMA interface. Ideal for power and space-sensitive applications like secure MCU, IoT server, gateway and edge devices, these accelerators are the most versatile, complete crypto solutions that offer the best balance of size and performance available on the market.
For automotive applications, Rambus offers the same three-tiered CryptoManager architecture tailored to the needs of automotive customers. CryptoManager RT-7xx v3 Root of Trust family provides all the functionality for fully programmable ISO 26262 ASIL-D process, ASIL-B or ASIL-D safety mechanisms and ISO 21434 compliant hardware security modules. Dedicated CH-7xx/CC-7xx configurations offer automotive ISO 21434 compliance and ISO 26262 ASIL-B or ASIL-D safety mechanisms.
Configurations differ by cryptographic accelerators contained, protection mechanisms required, including DPA and FIA, and third-party security standard compliance. Rambus can optionally offer dedicated certification support packages to its CryptoManager Hub licensees that provide related certification documentation, test scripts, and dedicated support to achieve FIPS 140-3, SESIP, PSA RoT Component, ISO 26262 (ASIL-B or ASIL-D), ISO 21434 (Cybersecurity) certification with your product embedding a CryptoManager.
“At Untether AI, we provide energy-centric AI inference acceleration from the edge to the cloud, supporting any type of neural network model. Our at-memory compute architecture solves the data movement bottleneck, resulting in high-performance, low-latency inference acceleration without sacrificing accuracy,” said Renxin Xia, Vice President of Hardware at Untether AI. “Ensuring the security of our solutions for data-at-rest and data-in-motion is essential. To address this, we need advanced protection and future-proof security measures. The Rambus CryptoManager Security IP solutions offer a comprehensive suite of security features that enable products like ours to meet the stringent security needs while ensuring the reliability and safety of our AI solutions.”
With over 30 years of security industry leadership, Rambus offers the broadest range of state-of-the-art security IP solutions available. Given the flexibility of the three-tiered CryptoManager Root of Trust architecture, it’s never been easier to get the perfect combination of features and integration tailored to the security needs of your application.
Highlights:
SAN JOSE, Calif. – March 10, 2025 – Rambus Inc. (NASDAQ: RMBS), a premier chip and silicon IP provider making data faster and safer, today announced the introduction of its next-generation CryptoManager Security IP solutions including Root of Trust, Hub and Core families. The CryptoManager Security IP offerings deliver progressively higher levels of functional integration and security, enabling customers to choose the level of security features and capabilities best suited to their unique requirements.
The CryptoManager Root of Trust delivers a fully-turnkey solution and offers the industry’s first Quantum Safe boot flow. The CryptoManager Hub provides the ideal combination of proven cryptographic building blocks for customers designing their own root of trust or secure processor. With support for a broad set of security functionality and certifications, Rambus CryptoManager Security IP solutions help customers accelerate the time to market of chips for the data center, AI and other advanced applications.
“The pace of value creation in the data center driven by AI is unprecedented, and the need to protect this value grows commensurately,” said Matt Jones, SVP and general manager of Silicon IP at Rambus. “The multi-tiered architecture of our new generation CryptoManager Security IP lets us serve a broader set of customers with solutions that provide an unrivaled level of flexibility and industry-leading protection of valuable hardware and data assets.”
“Rebellions builds energy-efficient AI accelerators optimized for Generative AI workloads in Data Center and Enterprise Inference applications,” said Sunghyun Park, co-founder & CEO of Rebellions. “Security is a critical component for ensuring the confidentiality, integrity, authenticity, and availability of data and devices. The CryptoManager solutions from Rambus offer a range of options to meet our performance, security, and area requirements, so we can fully address our customer application demands.”
CryptoManager Security IP solutions include:
More Information
CryptoManager Security IP products are certified to FIPS 140-3, SESIP, PSA, ISO 26262 and ISO 21434 for applications across data center, automotive, government and military. For more details, visit Rambus Security IP. Rambus will host a webinar “Implementing State-of-the-Art Digital Protection with Rambus CryptoManager Security IP,” discussing the application and implementation of CryptoManager Security IP products on April 16, 2025 from 10:00am – 11:00am PT. Additional info on the next-gen CryptoManager Security IP solutions including Root of Trust, Hub and Core families can be found on the Rambus blog, “Rambus CryptoManager Root of Trust Solutions Tailor Security Capabilities to Specific Customer Needs with New Three-Tier Architecture.”
The confidentiality and integrity of cryptographic key material is critical to maintaining system security. A hardware root of trust, such as the Rambus CryptoManager Root of Trust, is designed to securely generate, store, and employ cryptographic keys. Tortuga Logic has independently verified the policies surrounding access to keys stored within registers in the CryptoManager Root of Trust using its Radix pre-silicon security verification platform.